Malware & Ransomware
How Sandboxing Works: The Mechanics of Isolated Execution
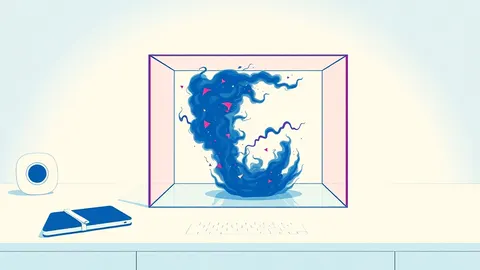
Sandboxing traps malware in a fake operating system, but advanced threats detect these artificial environments and refuse to execute.
Everything DataSafe Times has reported about malware analysis: 4 stories, newest first. Part of our Malware & Ransomware coverage.
Sandboxing traps malware in a fake operating system, but advanced threats detect these artificial environments and refuse to execute.
Viruses require user action to replicate, whereas other malware types execute silently and autonomously within system memory.
Mobile malware often operates silently within legitimate applications, bypassing standard security checks by exploiting the permissions you grant during installation.
The payload is the malicious code that runs after initial access, meaning detection often fails until the damage is already occurring on the system.