Vulnerabilities
SBOM Misconceptions: What a Software Bill of Materials Actually Does
An SBOM lists component names and versions but provides zero security value until you integrate it with vulnerability databases and policy engines.
An SBOM lists component names and versions but provides zero security value until you integrate it with vulnerability databases and policy engines.
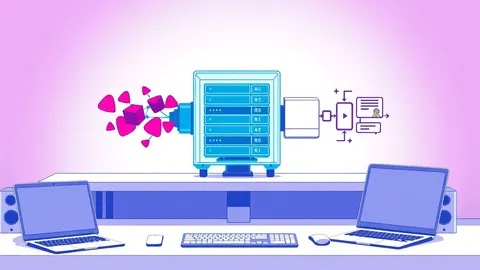
Parameterized queries separate code from data at the database protocol level, preventing injection by forcing the engine to treat all input as literal values rather than executable instructions.
Path traversal exploits rely on the gap between how a server interprets a file path and how the operating system resolves that same path on disk.
Treating parameters as mere input sanitization creates blind spots where logic flaws and type confusion bypass protections entirely.
Fuzz testing reveals hidden memory errors and logic flaws by feeding programs with malformed data until they crash, often finding bugs static analysis misses.
Fuzz testing exposes logic errors by feeding malformed data to inputs, revealing crashes that manual review and standard unit tests consistently miss in complex code.
Transport networks use industrial control systems that run on outdated software, creating hidden entry points for attackers to disrupt physical movement rather than just steal data.
Page builders fragment code execution, creating blind spots where standard security audits fail to detect logic flaws and injection vectors.
Moving security checks earlier in the pipeline reduces remediation costs and prevents runtime failures that are expensive to fix later.
Phishing simulations measure human error rates to prove that technical controls like DKIM and DMARC cannot stop every attack vector targeting user judgment.
Privacy rights shift control from data collectors to individuals, allowing you to demand deletion or correction of stored information through standardized legal channels.
Your device aggregates local sensor data with cloud profiles to predict behavior, creating a dossier you never explicitly authorized.
Role based access control decouples permissions from identities, while access control lists bind rights directly to user names, creating different maintenance burdens.
Potentially unwanted programs hide inside legitimate installers to alter system settings and generate revenue without explicit user consent.
Mobile malware often operates silently within legitimate applications, bypassing standard security checks by exploiting the permissions you grant during installation.
Platforms sell your inferred interests, not just your posts, creating a permanent record that persists long after you delete the account or change your mind.
Public Wi-Fi risks stem from misconfigured client settings rather than malicious access points, turning your device into an open book for anyone on the local network segment.
Your cloud provider cannot read your files because the encryption key never leaves your device, rendering the data useless to attackers.
Your approval button is a race condition against human reflexes, and speed defeats security when notifications arrive in rapid succession.
Small organizations are targeted not for their data value, but because their security controls are predictable and their backups are often reachable from the compromised network.
Attackers use voice calls to bypass technical controls, exploiting human trust and verification gaps that software alone cannot close.
Most tracking does not require cookies; it relies on the unique fingerprint your browser sends with every network request.
The cloud provider secures the physical hardware and virtualization layer, but you remain liable for every configuration error within your own tenant environment.
Most botnet infections remain invisible to users because the malware throttles its traffic to stay below the threshold of standard network monitoring alerts.